See your own findings in minutes.
Connect a cloud account with a read-only role and run 2,500+ checks. Free for 7 days, no credit card, no account limit.
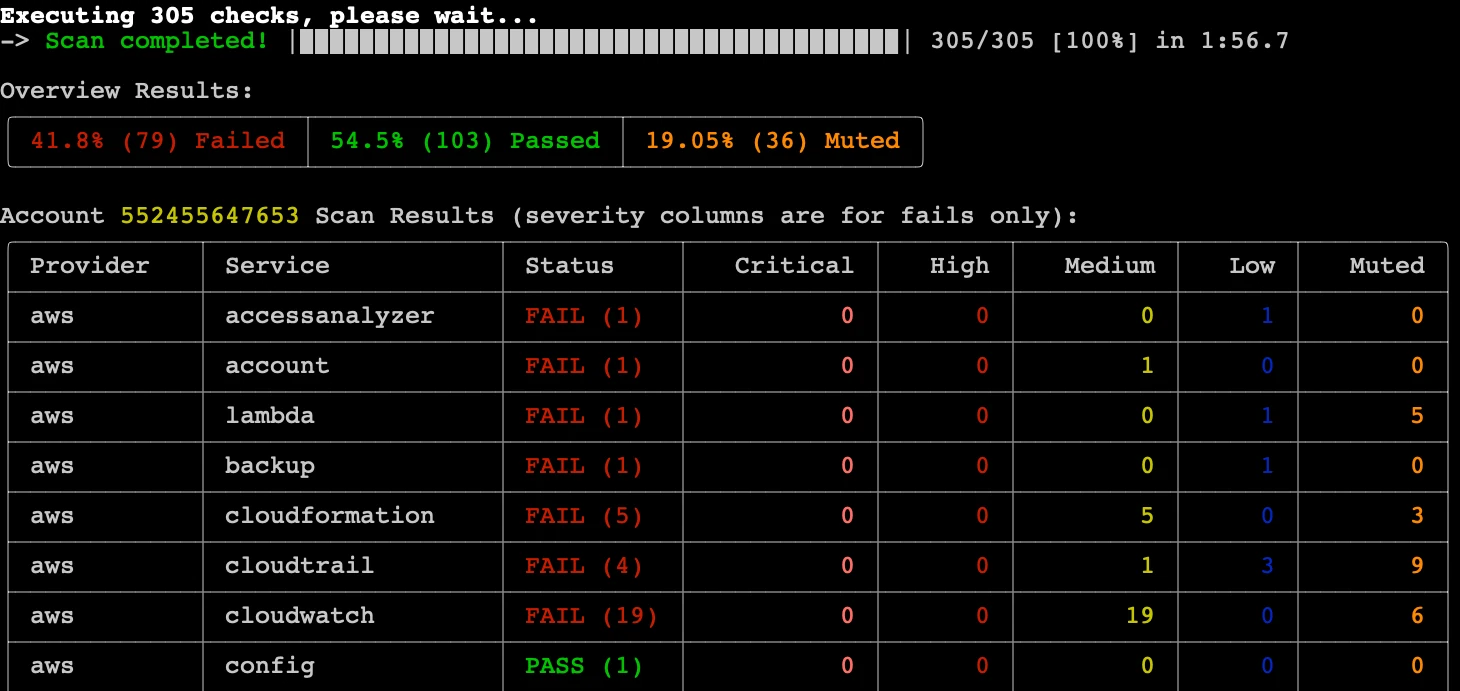
A sample of the requirements
Each requirement is mapped to automated checks. Prowler Cloud scores every requirement, tracks it over time and exports the evidence for your auditor.
Versions available
FAQ
Yes. Prowler maps 458 checks to Prowler ThreatScore across Alibaba Cloud, Amazon Web Services (AWS), Google Cloud, Kubernetes, Microsoft 365, Microsoft Azure.
Create a free Prowler Cloud account at cloud.prowler.com, connect your accounts and open the compliance view to see your Prowler ThreatScore status and export evidence for your auditor.
Framework data comes from Prowler Hub and is updated daily.
Connect a cloud account with a read-only role and run 2,500+ checks. Free for 7 days, no credit card, no account limit.