The open cloud security platform
Find every risk. Fix the few that matter first.
Clouds, AI infrastructure, SaaS apps, identity, Kubernetes and IaC: 2,500+ open checks across 34 providers, mapped to 100+ compliance frameworks. And any AI agent can put them to work as your security engineer through the Prowler Cloud MCP Server.
Trusted by security teams at
The most widely used open-source cloud security tool.
Every check is public. Read the code before you trust it.
CIS, SOC 2, ISO 27001, PCI DSS, NIS2 and more, from one scan.
Agentic security
Any AI agent can be your security engineer.
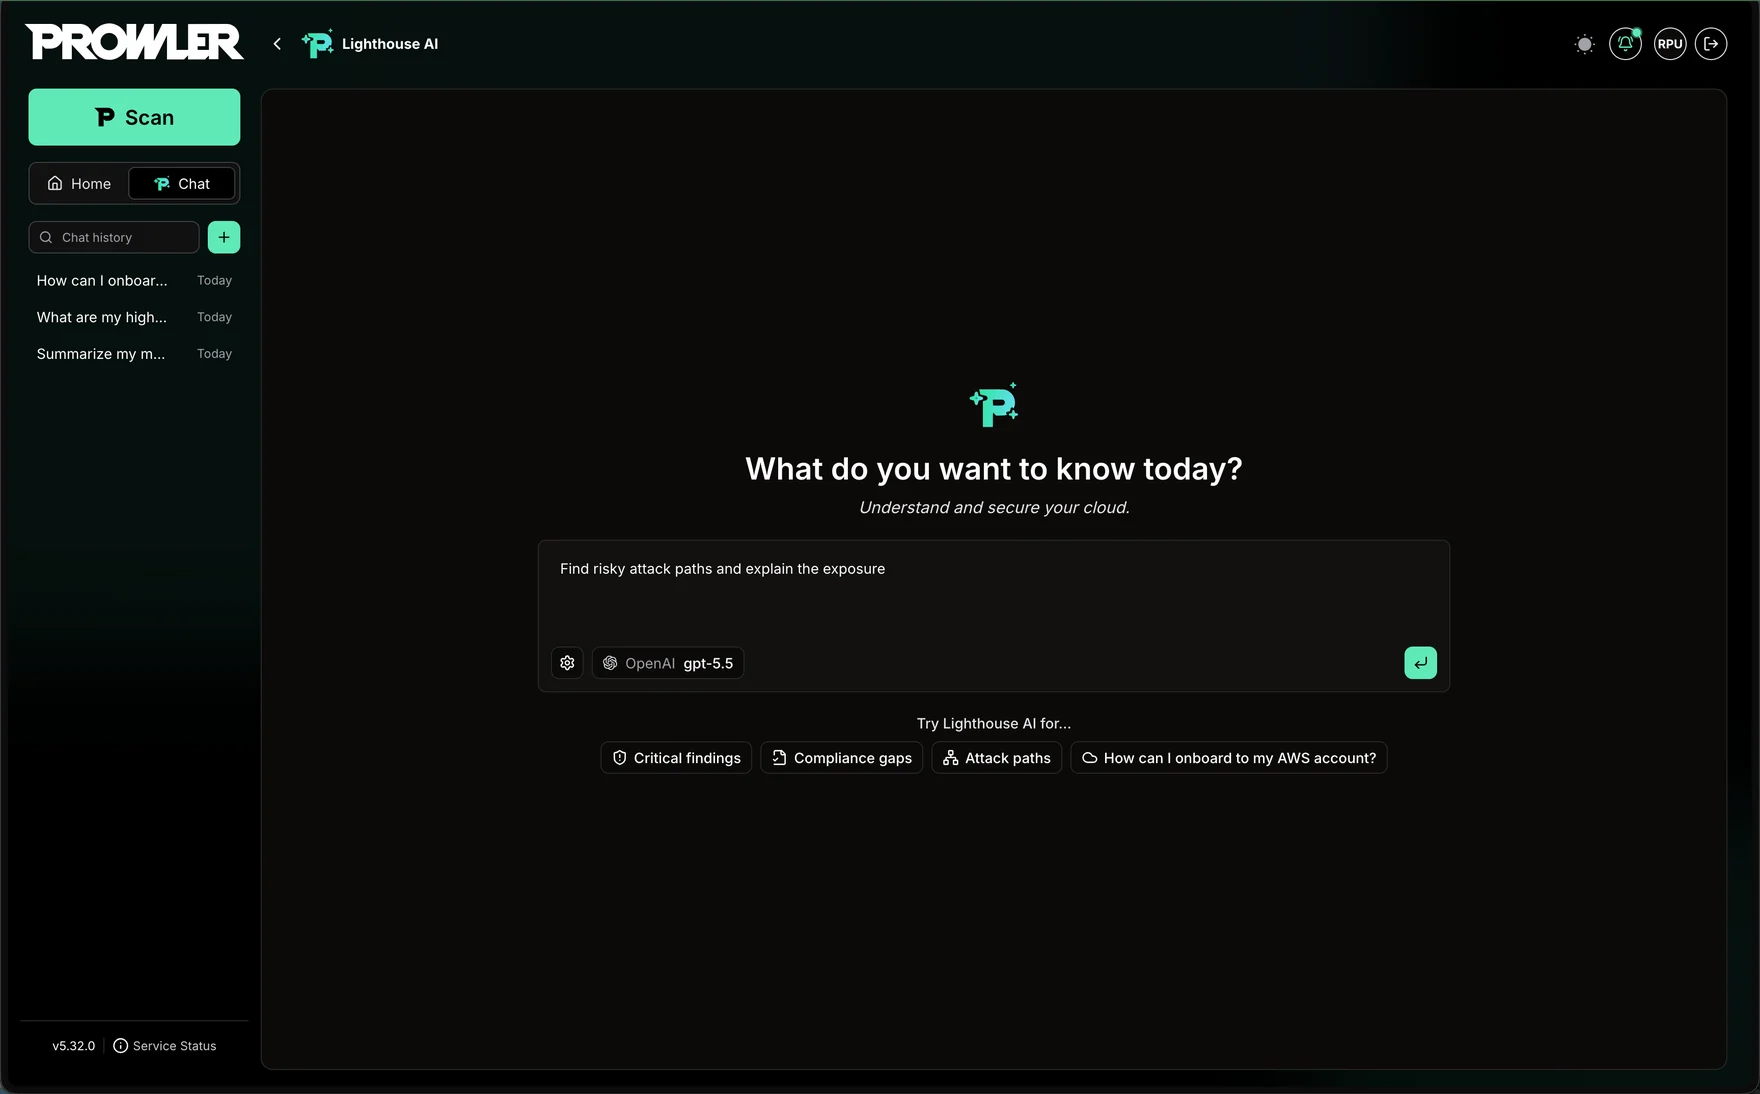
Connect Claude, Codex, Cursor, Copilot or any MCP client to Prowler Cloud with one API key. Your agent can scan, triage, explain, map to compliance, open tickets and write the fix, across everything Prowler covers.
- Every premium feature is a tool. Findings, attack paths, compliance, scans, mutes, Jira and alerts.
- Your agent proposes fixes in your repo for review. Cloud scans use read-only access. Prowler Realtime applies fixes only when you enable automatic remediation and configure a dedicated role.
- Same guardrails as your team. The API key carries your user's role, so your agent can do only what you can.
- Humans and agents on one control plane. What the agent triages, your team sees in Prowler Cloud.
How it works
From sign-up to your first prioritized finding in minutes.
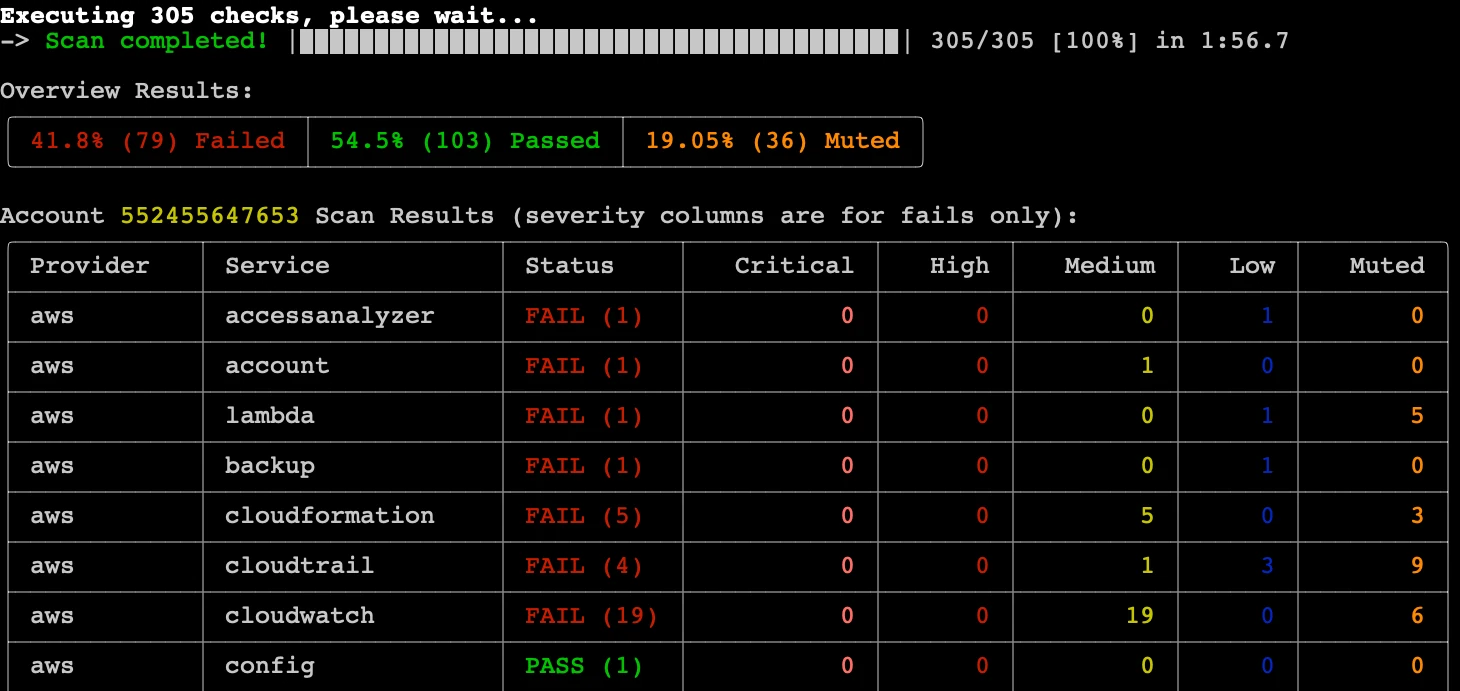
The same open-source engine runs in the CLI and in Prowler Cloud, so what you test locally is what runs in production.
- 01
Connect
Add an account, or a whole AWS, Azure or GCP organization, with a read-only role. No agents.
~2 min - 02
Scan
2,500+ checks run across every account and map to 100+ compliance frameworks at once.
minutes - 03
Prioritize
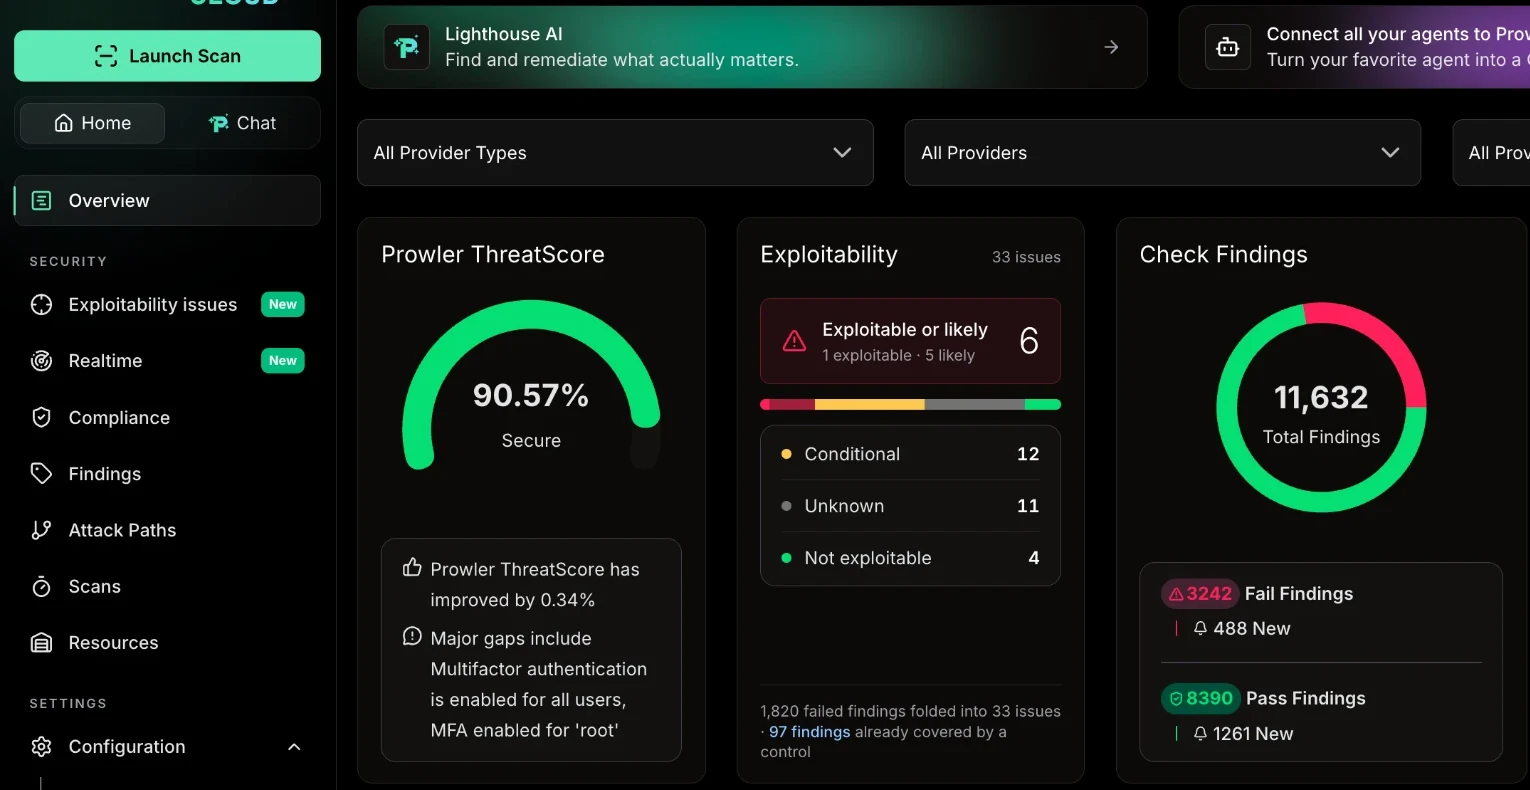
ThreatScore, toxic combinations and attack paths show what is actually exploitable.
automatic - 04
Fix
Lighthouse AI explains each fix. The Autonomous Fixer opens it as a pull request.
your pipeline - 05
Verify
Rescan a single finding to confirm the fix held, and track posture over time.
continuous
Product tour
Prowler finds everything. Prowler Cloud understands what matters.
Prioritized findings, attack paths and toxic combinations, continuous compliance across clouds, Lighthouse AI and the MCP Server for your agents.

Example tenant. Prowler maps findings to frameworks and produces evidence for your auditor.
The open catalog
Every platform we cover. Every check, in public.
Closed platforms ask you to trust a black box. Prowler publishes the code of every check on Prowler Hub, so your team can read exactly what runs before it touches your accounts. Pick a platform to see its checks.
Clouds
 AWSPublic exposure, IAM privilege, encryption and Bedrock→
 Microsoft AzureEntra ID, Defender, storage and network exposure→
 Google CloudIAM, Cloud SQL, storage exposure and Vertex AI→
 Alibaba CloudRAM access, OSS buckets, logging and secrets→
 Oracle CloudIdentity, network exposure and audit logging→
 OpenStackCompute, storage encryption and network boundaries→
 E2E NetworksPublic nodes, databases and security groups→
 Huawei CloudIAM, VPC exposure, KMS and logging→
 LinodeFirewalls, public exposure and backups→
 StackITIaaS exposure, object storage and SKE→
 NHN CloudNetwork and compute exposure→
 ScalewayIAM and access keys→
 VMware VCFPrivate cloud hardeningCloud
AI stack
 LLM red teamingPrompt injection, PII leaks, jailbreaks and bias→
 ClaudeWorkspace access, API keys and data controlsCloud
 OpenAIOrg access, API keys and data controlsCloud
 Amazon BedrockGuardrails, agent roles and model accessCloudBedrock AgentCoreAgent identity, tools and runtime accessCloud
 Vertex AIModel endpoints, notebooks and service accountsCloud
 Azure AI FoundryAI services access and private endpointsCloud
 MCP securityMCP servers, tools and permissionsCloud
Code and containers
 Infrastructure as CodeTerraform, Kubernetes and Dockerfile misconfigurations before deploy→
 KubernetesAPI server, kubelet, RBAC and etcd hardening→
 GitHubBranch protection, Actions, secrets and supply chain→
 VercelDeployment protection, domains and team access→
 Container imagesVulnerable and misconfigured container images→
 SupabaseRow-level security, keys and exposureCloud
 LovableApp exposure and Supabase backendsCloud
SaaS and identity
 Microsoft 365Entra, Exchange, Teams and SharePoint sharing→
 Google WorkspaceGmail, Drive sharing and admin security→
 CloudflareZone TLS, WAF, DNS and Workers→
 OktaMFA, sign-on policies, API tokens and apps→
 MongoDB AtlasNetwork access, encryption and backups→
 DatabricksWorkspace access, clusters and secretsCloud
Every platform has its own page, and every check is public on Prowler Hub with the code behind it. Browse all checks on Prowler Hub ↗ · "Cloud" means covered in Prowler Cloud.
Built for your security review
Win the paperwork, not just the demo.
Read-only, agentless
Connectors and Lighthouse AI analyze your cloud. They never modify it.
SOC 2 Type II
Plus the AWS Foundational Technical Review, passed. Report under NDA.
AES-256 and TLS 1.2+
Encrypted at rest and in transit, with SAST, DAST and SCA on every build.
Your data residency
Private Cloud keeps everything in your VPC, data center or air-gapped network.
Prowler love
Don't take our word for it.
“One of the best open-source and cost-effective cloud posture management tools out there. Call it ‘CSPM’ or whatever four-letter acronym you prefer, they do it all.”
“Security Hub native integration with Prowler is now the recommended solution for sending findings from Prowler.”
“Prowler stands out as a top-tier tool in terms of functionality and community engagement, offering robust features comparable to those of commercial solutions.”
“Can't thank you enough for this tool. Default go-to tool for cloud security, just as nmap was for every netsec folk.”
“I was pretty amazed by the tool. I'd definitely recommend this open source tool to audit your AWS account to fix security issues.”
“Prowler makes it super easy to identify vulnerabilities, improve security posture, and stay compliant with cloud best practices.”
Prowler Academy
Learn cloud security the way practitioners do it.
Free, hands-on courses from the team that writes the checks. Go from your first scan to prioritizing risk, proving compliance, writing custom checks and putting AI agents to work. Certification exams are $199.
See your own findings in minutes.
Connect a cloud account with a read-only role and run 2,500+ checks. Free for 7 days, no credit card, no account limit.