See your own findings in minutes.
Connect a cloud account with a read-only role and run 2,500+ checks. Free for 7 days, no credit card, no account limit.
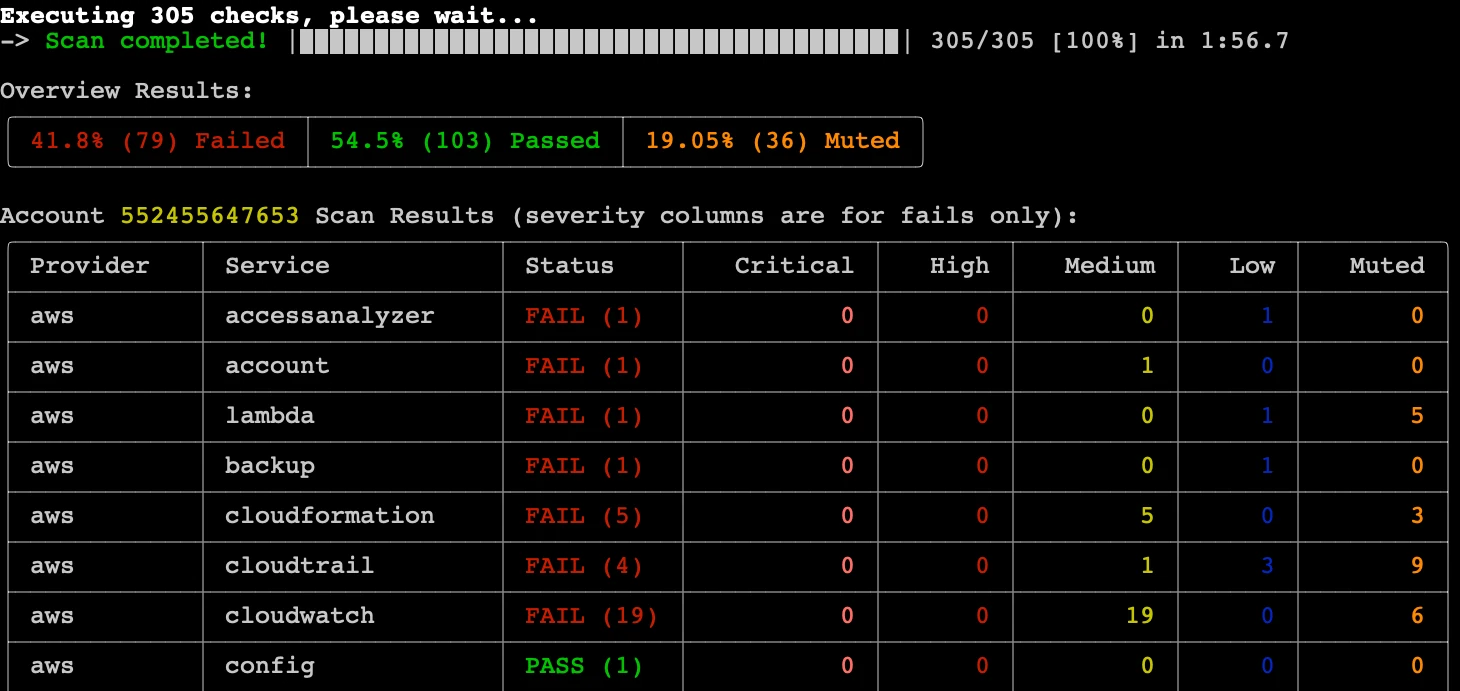
A sample of the checks
A few of the highest-severity checks. Prowler Cloud runs all of them continuously, ranks every finding by real risk and shows you how to fix it.
Services covered
Compliance frameworks
Map findings to your own frameworks with the Prowler Registry.
FAQ
Yes. Prowler runs 27 open-source checks for container images, including 7 critical and 13 high severity checks.
Create a free Prowler Cloud account at cloud.prowler.com and connect your container registry with read-only access.
Check data comes from Prowler Hub and is updated daily.
Connect a cloud account with a read-only role and run 2,500+ checks. Free for 7 days, no credit card, no account limit.